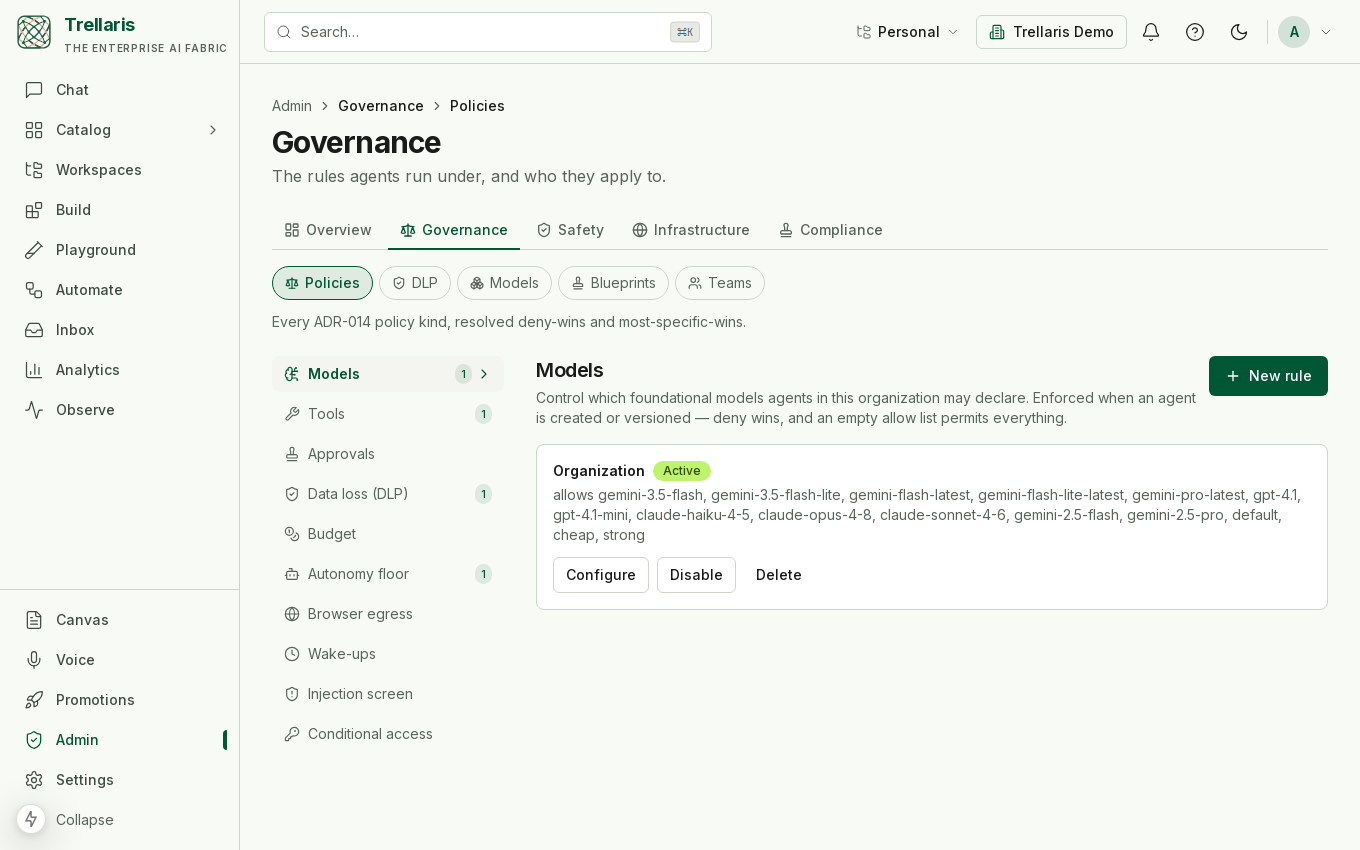
Tool allowlist
This is one policy kind in the ADR-014 governance engine. Policies resolve most-specific-wins with deny-wins at a tie, across scopes that run agent → user/role → workspace → team → org. Rules of the same kind combine rather than replace, so what matters is which rules exist, not which policy row holds them.
What it does
A tool-allowlist policy controls which tools an agent may actually call at run time, and which MCP-server tool surfaces are reachable. A denied tool is hidden — the agent never sees it in its tool list, so it cannot try and be refused; it simply is not there.
How it resolves
Allowlists intersect across scopes: a narrower scope can remove a tool the org allows but can never add one the org withholds. That is what lets a team tighten its own agents without being able to widen past the org's line.
Relationship to the agent's declaration
An agent declares the tools it wants in Agent.md; the policy
decides which of those it actually gets. The effective set is the
intersection of the declaration and every allowlist in scope.