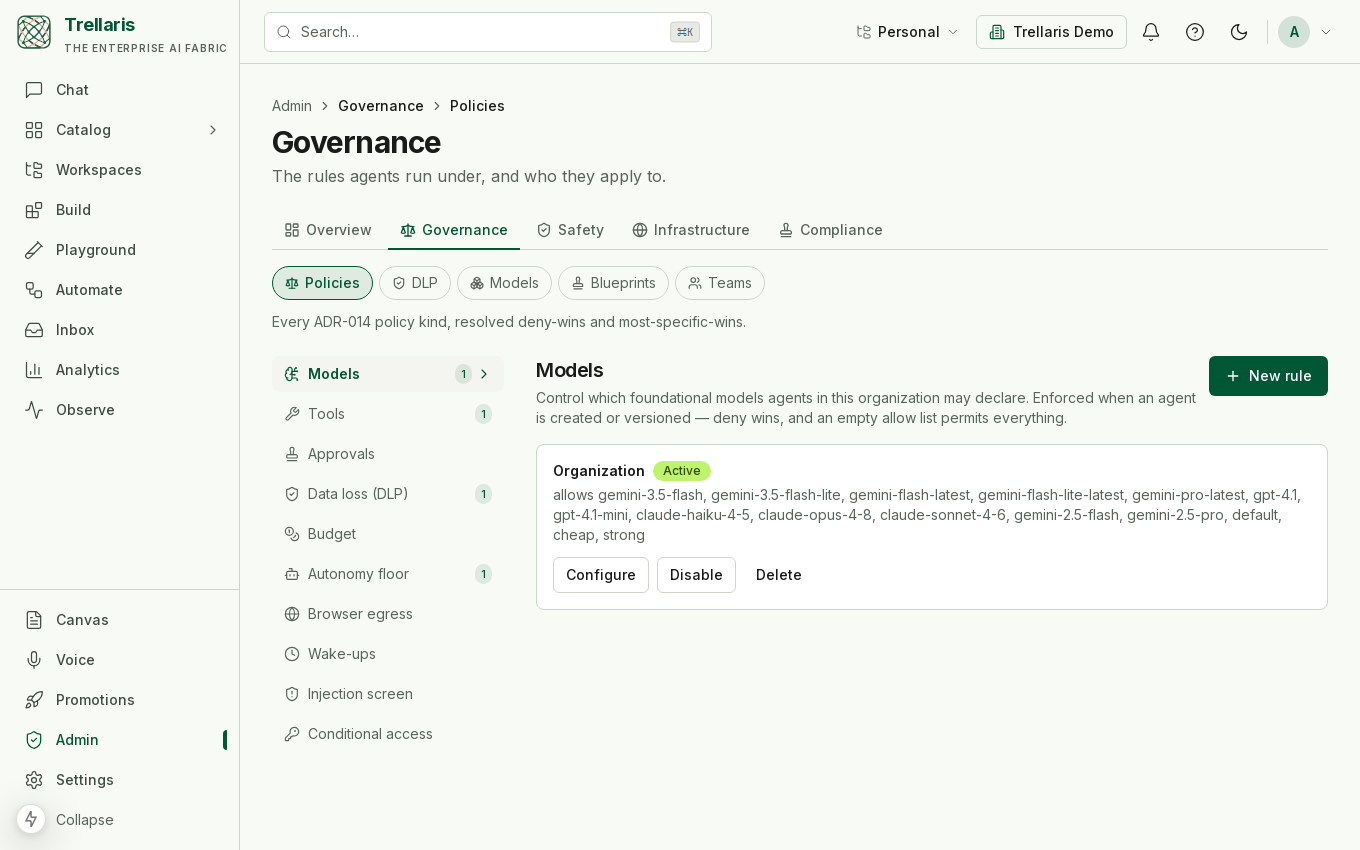
Model allowlist
This is one policy kind in the ADR-014 governance engine. Policies resolve most-specific-wins with deny-wins at a tie, across scopes that run agent → user/role → workspace → team → org. Rules of the same kind combine rather than replace, so what matters is which rules exist, not which policy row holds them.
What it does
A model-allowlist policy controls which models an agent may run on. A definition that names a model outside the allowlist is refused at validation time — you cannot save an agent that could never legally run — and the gateway enforces it again at call time.
Why validate early and enforce late
Catching it at validation gives the author an immediate, specific error instead of a run that fails in production; enforcing at the gateway means a policy change after the fact still holds, even for an agent authored when the model was allowed.
Tiers, not just names
Agents usually name a tier — default,
cheap, advanced — which the gateway maps to a
concrete model per org. The allowlist can constrain the concrete models a
tier is allowed to resolve to.