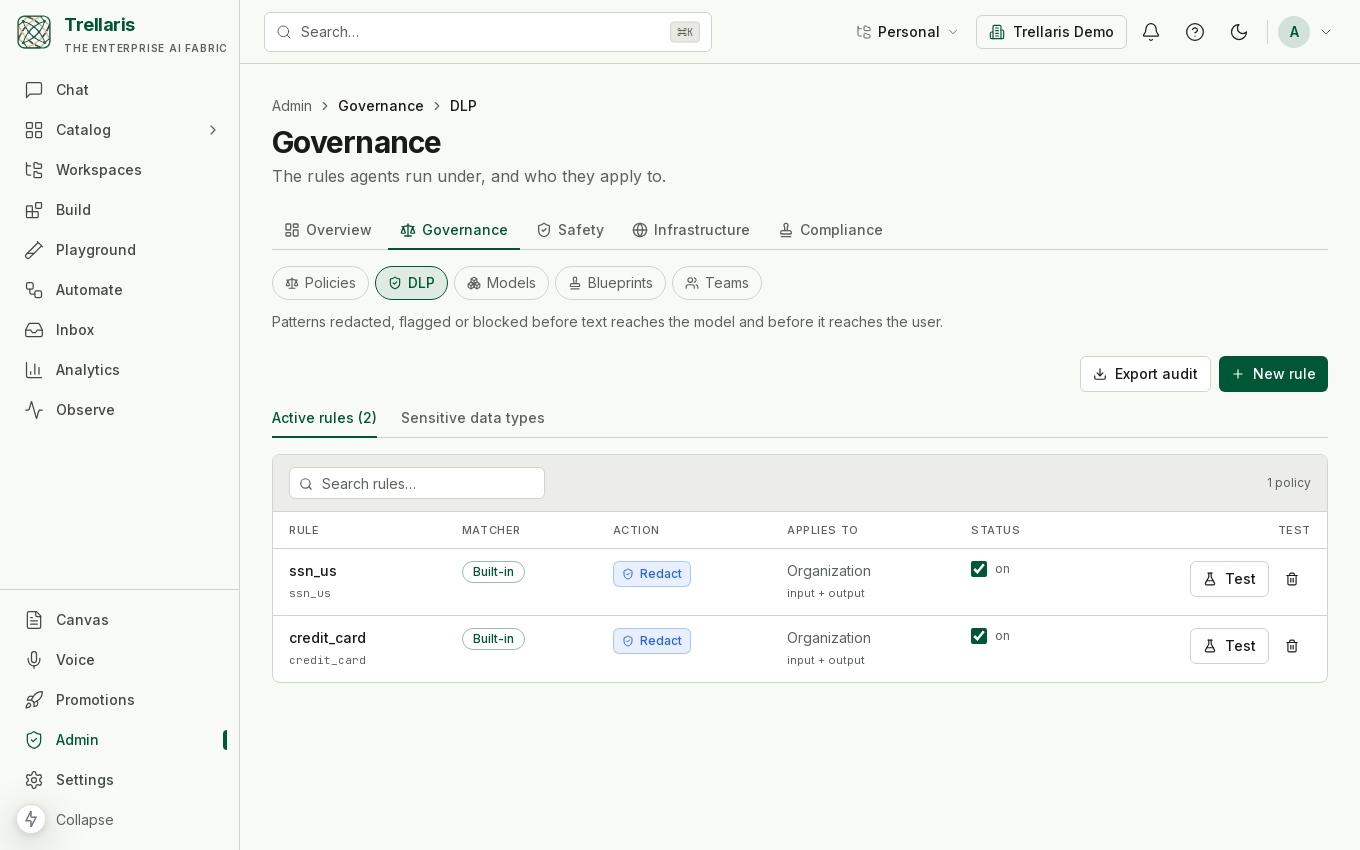
DLP (data-loss prevention)
This is one policy kind in the ADR-014 governance engine. Policies resolve most-specific-wins with deny-wins at a tie, across scopes that run agent → user/role → workspace → team → org. Rules of the same kind combine rather than replace, so what matters is which rules exist, not which policy row holds them.
What it does
A DLP policy redacts sensitive spans from text. It runs at the model boundary — on input before the model sees it and on output before a person or a tool does — and at the gateway on tool input and output, so sensitive data is caught whichever way it flows.
Matchers
Built-in matchers cover common identifiers — SSN, credit card (Luhn- checked), IBAN, email, phone, AWS keys, private-key blocks — and a policy can add regex rules. Each rule chooses an action: redact (replace with a marker) or, across scopes, the strongest action wins.
Test before you enable
The admin DLP console lists every rule in the org as one flat table and lets you test a rule against pasted text in a right-docked console. The simulator walks the same rules in the same order with the same matchers as the live engine, so what you see is what will happen — and nothing you paste to test is stored.